I’ve done Web3 security full time for almost 3 years.
200+ High and Medium bugs found
$1.6B+ TVL secured
100+ audits done
It taught me one thing:
Becoming a skilled Web3 auditor is extremely hard.
Auditors often ask me:
“Is it still possible to become an auditor in 2026?”
It’s much harder now.
But even with AI, the private audit market is booming. The demand is crazy.
So here’s how I’d become an auditor in 2026:
Why you should pick a niche
Which protocols to learn
How to get private audits
Let’s go.
1. Why I’m pushing Solana
Early in my career, I was scared of Rust.
It felt like the next level.
Then one request changed everything:
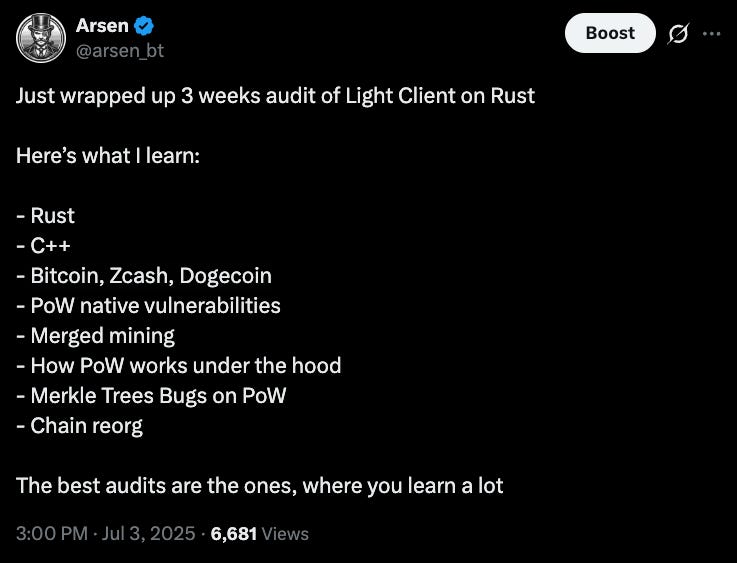
My first Rust audit. A Bitcoin light client.
3 weeks to finish it
I learned Rust and C++ on the job
I hunted bugs across Bitcoin, Zcash and Dogecoin
I understood that Rust, and most of this tech, isn’t that complex.
You just need to get your hands dirty ASAP.
Today, 90% of my work is Solana and Rust.
It’s the future of DeFi
When I started, most audits, contests and bounties were on EVM.
Times have changed. EVM is still the biggest market.
It’s also the most crowded:
Thousands of auditors
Hundreds of AI audit bots
Tons of EVM audit resources
That makes the barrier high. Entering EVM isn’t the same as it was 2 years ago.
Few people look at the niche, where there are fewer resources and fewer auditors.
Solana is one of the most promising directions.
Solana made $143M in app revenue in August.
Ethereum did $47M in the same month.
That’s 3 times less. DefiLlama numbers.
Auditors who can work on Solana earn more by default.
Why?
Not many people know Solana, but the demand keeps growing.
Demand is booming
Private audits are cooking.
More and more really strong projects are building on Solana:
Projects & institutions are coming into play
The Solana dev community is very solid
Cheap tx and gas
We even saw an L1 on Cosmos close and move to Solana.
This makes Solana the ideal next Top-1 blockchain.
If I were starting out today, I’d go to Solana.
It’s where the next level is.
How to learn Solana the right way
1 core rule to understand.
You shouldn’t spend too much time in theory.
You shouldn’t learn all of Rust or do a Rust course.
What you should do instead is very simple:
Open the RareSkills book
Open Blueshift
Spend 2-3 days reading Rust & Solana
At this step, you need the bare minimum.
Don’t learn it by heart. Just get a strong 1st overview.
Make sure you understand the following concepts:
How the account model works
What a PDA is
What a CPI is
What rent is
What an instruction is
What Anchor is
That’s enough to start reading the code.
Afterwards, we move to the more complex part.
2. Which protocols to learn
You know Solana now. You think you did a lot already.
But the hardest part is about to begin.
Soon you’ll audit projects that hold billions in TVL.
You need to work like a real professional. But how?
Learn 1 domain by heart
By domain, I mean one type of DeFi protocol:
CLMM, propAMM
Lending & borrowing
Perpetual futures
Virtual machines / nodes
Early in my journey, I jumped from contest to contest.
I didn’t stick to any domain.
One week I audited cross-chain. The next week, lending.
Nothing stuck.
Results appeared only when I went 1 domain at a time.
Only then did I understand the real game of audits.
Finding creative bugs by knowing the system well.
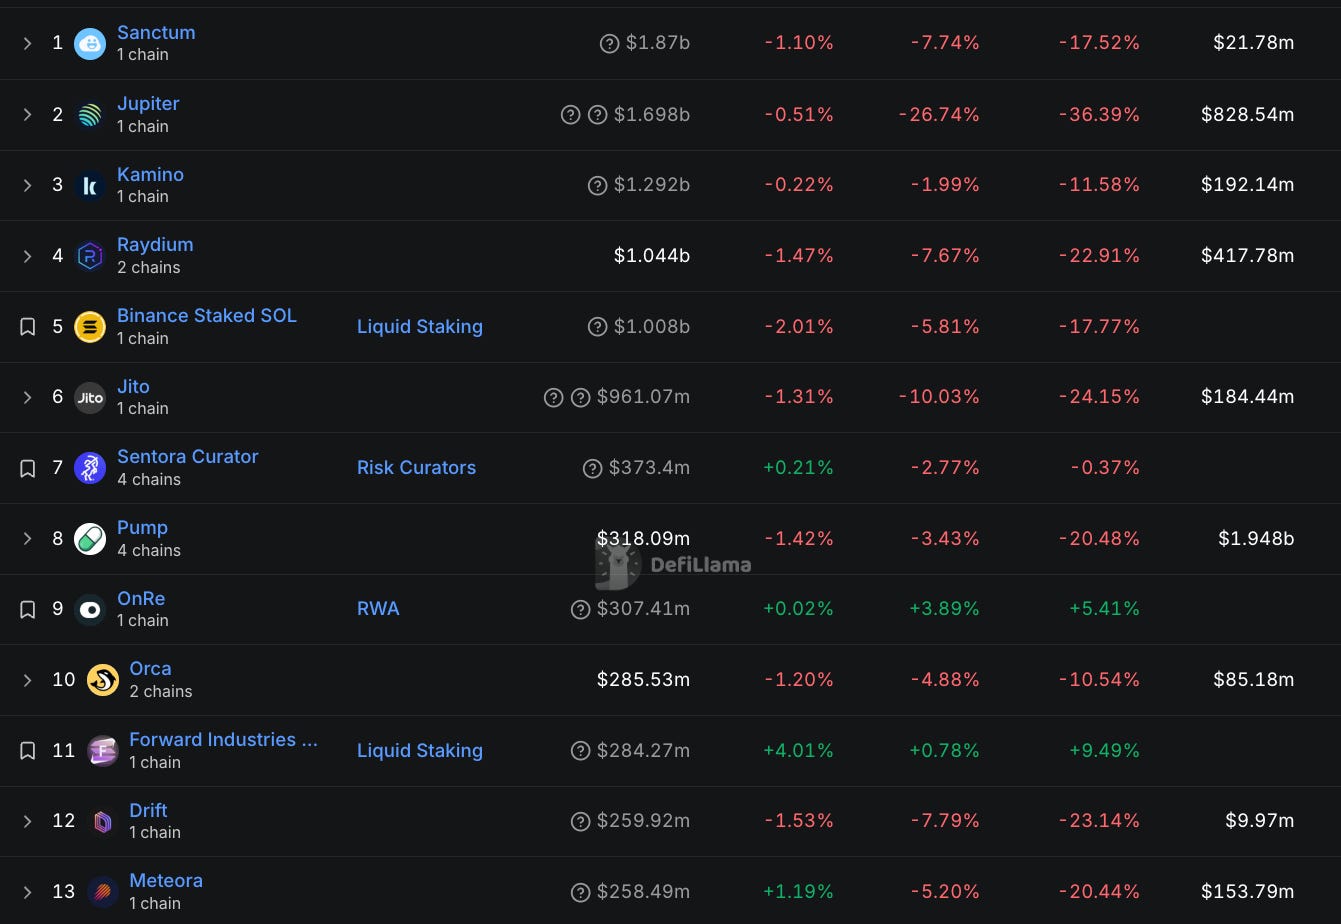
Just go to DefiLlama and check the top projects out there
Those are your 1st targets to audit.
Here's the top of that list:
Repeat for 90 days & save the knowledge
Pick one domain. Then:
Hunt only that domain for 90 days
Read the code
Study past exploits / reports
Record observations
Make the right notes
After you read this 1st project, you’ll gain valuable knowledge: how the core protocol works & what bugs it has
Then, make sure you save all notes in your DB, and tune your AI with this knowledge
That gives you an assistant that knows:
Major bugs you found or missed
Patterns that repeat across codebases
Implementations the devs made
Every structured note
30 retros later, you see patterns nobody else sees.
Wide gets you nowhere. Depth gets you paid.
3. How can I earn?
No one knows you
When you enter Web3 Security, no one knows you.
Bounties are harsh. Not everyone pays it.
So how can you earn?
By building yourself as a professional auditor.
Public portfolio
Strong X account
Proven record / Bugs found
It takes a lot of work to build those 3, but it’s exciting.
Eventually, if you stick to these 3, you will make it.
Are you a real professional?
Show that you can find bugs.
With and without AI, doesn’t matter.
It should be a real skill.
In 2026 it’s harder, due to the lack of dedicated contests.
That’s why I advise the following:
Find live projects and bounties
Hunt the bugs there by heart
Submit them to the team
Build your portfolio from these findings
Hopefully get paid (it’s not the main goal)
Repeat
Once you have a public record of 10-20 H/M findings in live projects, you’ll know the game, and you’ll be ready for private audits.
Pitch yourself
You should be a known professional in your own niche.
Once that’s set up, share your experience:
Write post-mortems
Write technical articles
Write tweets with your advice
Share the knowledge, inspire others, pitch yourself.
Afterwards, DM firms for private engagements.
Hunt the opportunities wildly.
And your first $3K private deal will be done.
If you want to do this with me, my Solana Audits Bootcamp starts Nov 23. Four weeks on real code, with a live call every week.
Live bonus: join before Sunday, Nov 8 and you get a 30-min 1:1 call with me. We plan your 4 weeks.
https://www.arsen.ac/web3-auditor-course
— Arsen