“How do I get audit experience if nobody will hire me?”
You keep studying.
Reports, docs, random threads.
But nothing tells you whether you can actually find a real bug.
You’re not short on information.
You’re short on a codebase with your name on the work.
Today I’m sharing the 4 ways to get audit experience with no clients.
Shadow audit one big protocol nobody pays you for
A live protocol doesn’t care whether someone hired you.
It gives you everything a paid engagement does:
the same flows
the same money
the same code you’d read for a client
The only difference is that nobody told you to open it.
So pick one lane and go deep on that, not on five:
lending
CLMM
a launchpad
whatever actually pulls you
While you read it, study the past public reports on the same protocol.
Then check whether the same pattern lives somewhere else in the program.
You come out with something you own: a checklist of the integration bugs that hit every team plugging into it.
Integrators repeat the same mistakes. That checklist is your edge.
My first place came from exactly this kind of reading:
a new chain
a new language
the last days of the contest, out of ideas
docs read, every line in scope read
So I went into the integrations sitting outside the scope.
That’s where the High was. $8K, one unique finding.
Everyone read the same in-scope files.
Nobody opened the other side of the integration.
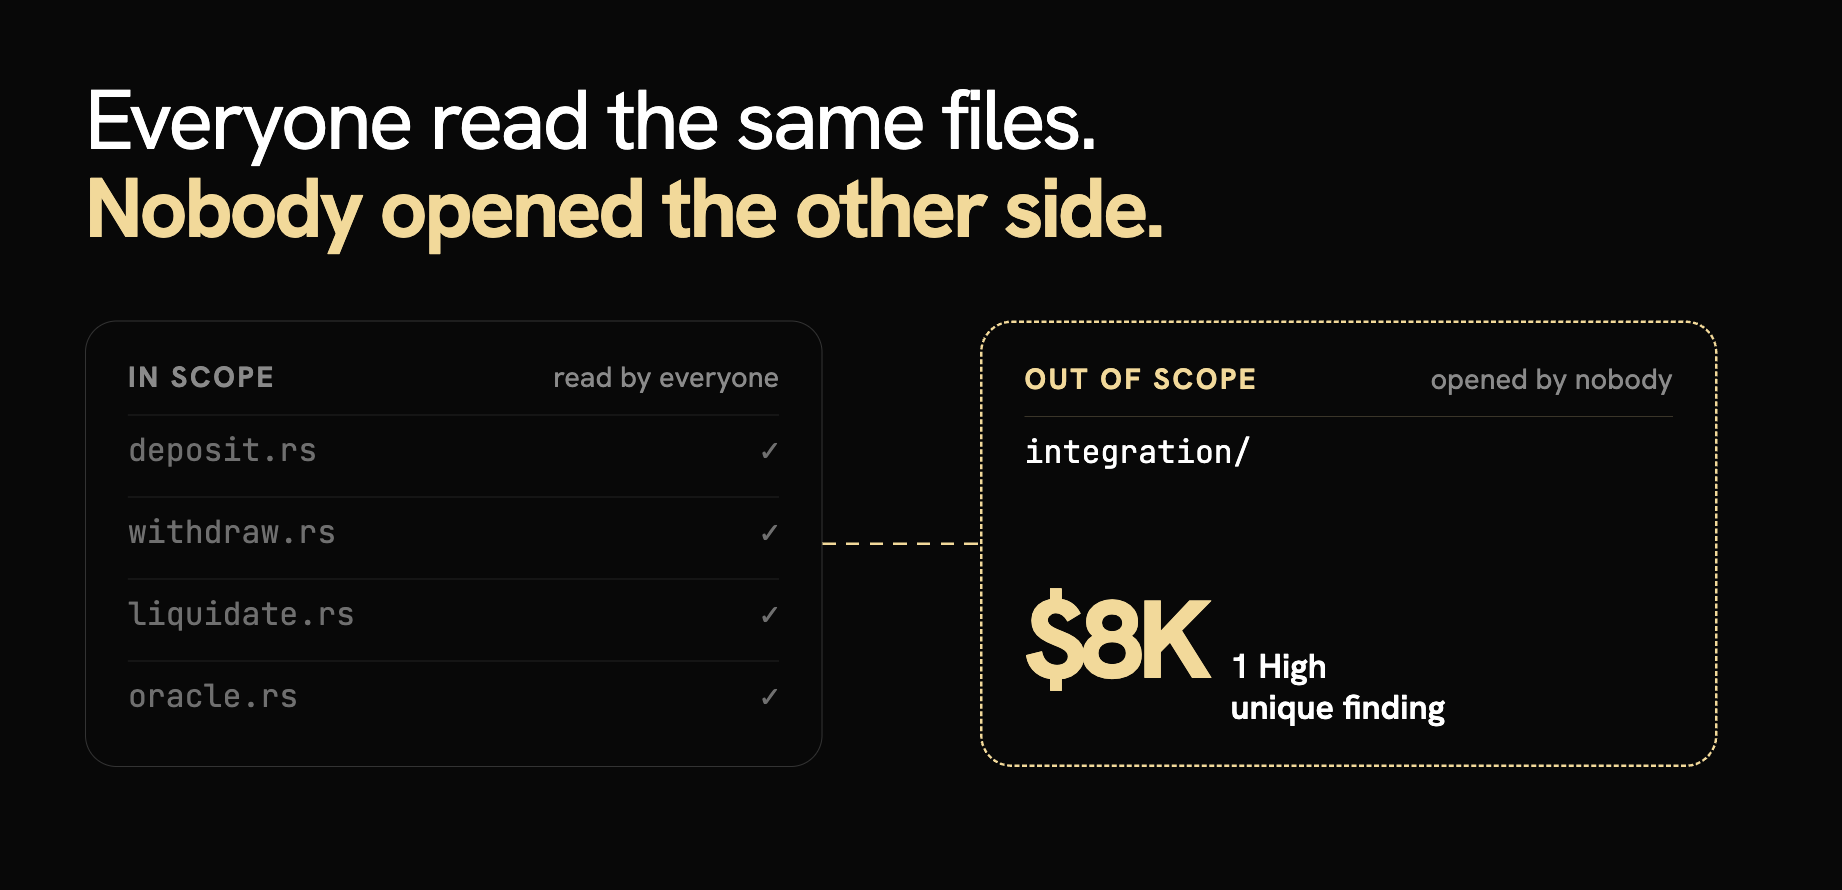
Out-of-scope code has nobody else in it. That’s the whole reason to read it.
Your move today:
Open one live Solana lending or CLMM program.
Write down its three core flows: deposit, withdraw, and the one the protocol earns on.
That list is your scope for the week.
Take whatever opens and keep every submission public
Stop waiting for the right contest to appear.
Contests are thin right now. So take what opens:
a bounty
a CTF
a one-off opening
All of it carries your name.
All of it counts as a portfolio before a client pays you.
Here’s what that looked like for me:
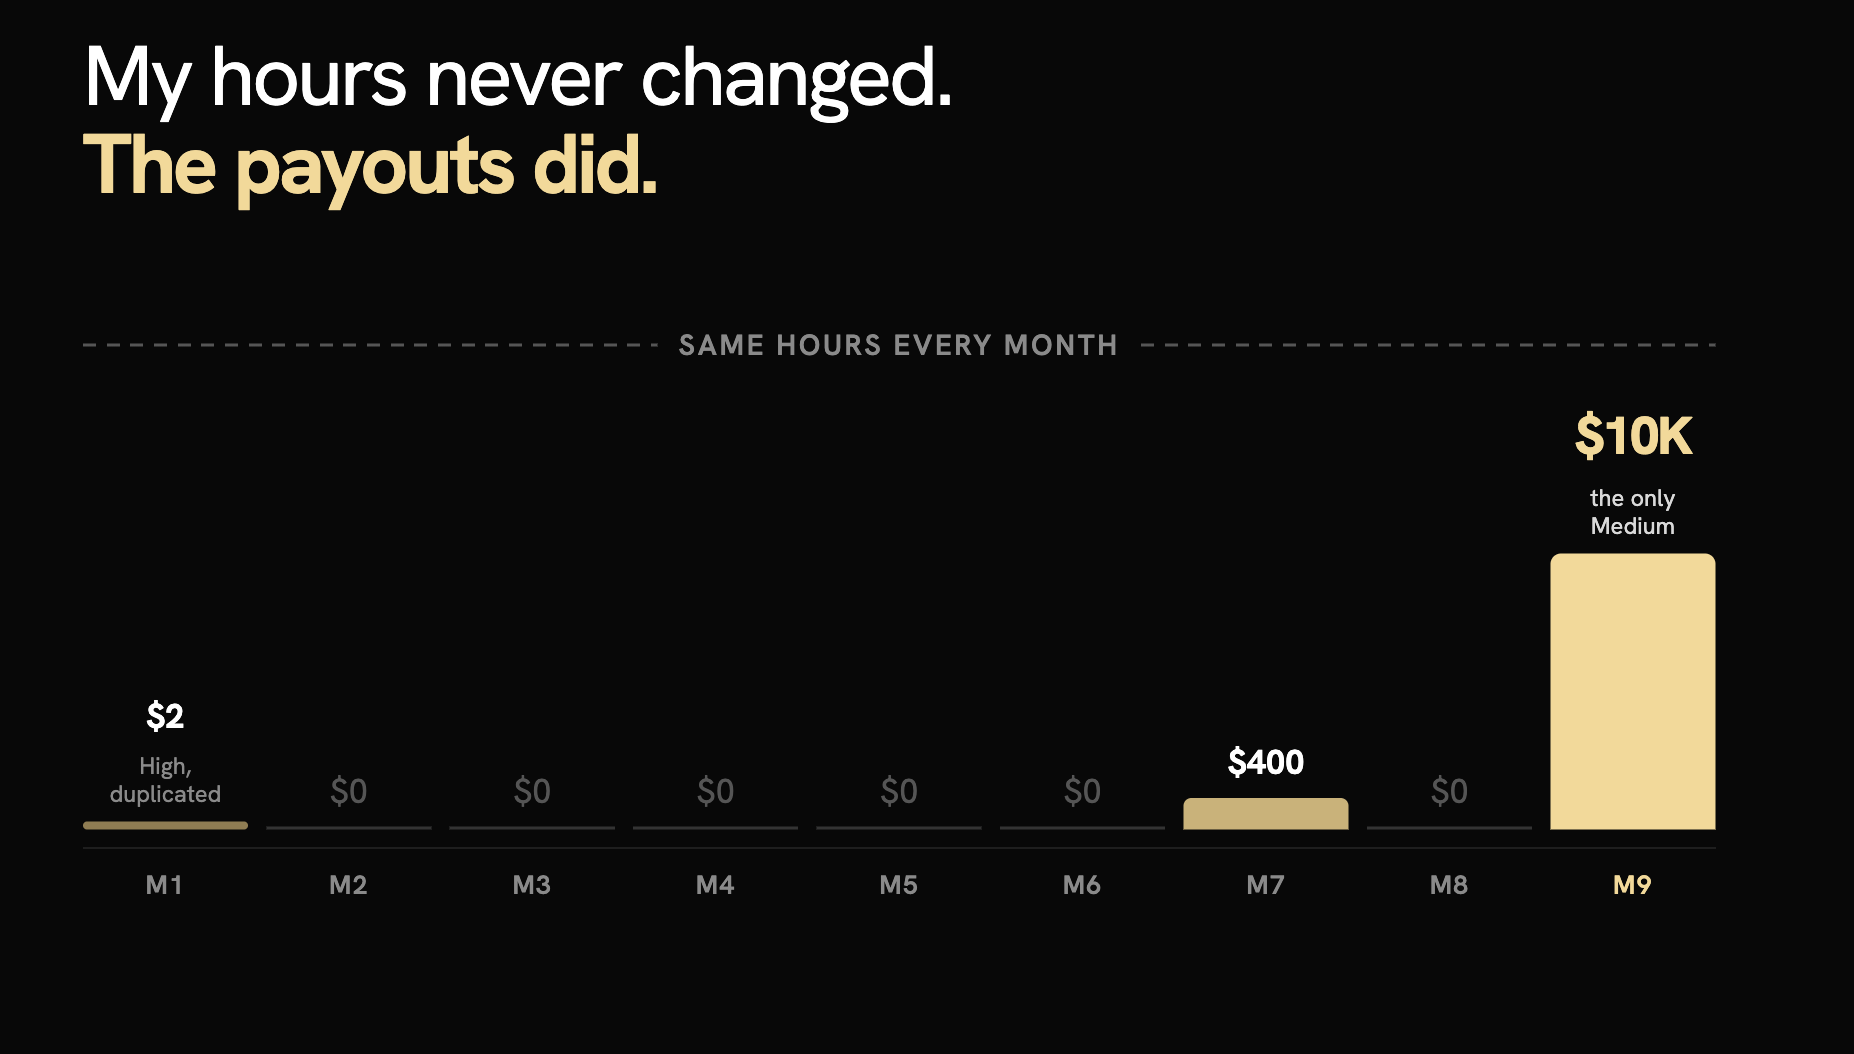
Contest 1: a High, duplicated. Paid $2.
Months 2-6: zero results. Same hours every month.
Month 7: $400.
Month 9: $10K for one Medium in a cross-chain codebase, the only Medium anyone found in the whole scope.
Later: a CTF, around 500 USDC and a job offer I turned down.
No client. No permission.
Every submission stayed public, and that’s the part that compounds.
The payout is not the point yet. The public record is.
Your move today:
Open one live bounty or CTF page.
Make two columns: flows in scope, flows outside it.
Start reading in the right column.
Ask teams directly for a free audit
Nobody is going to invite you.
An unpaid finding sits in a portfolio the same way a paid one does.
The team reading your report never asks what you charged.
I did free audits early. I just asked for them.
Some teams ignored me. Some said yes.
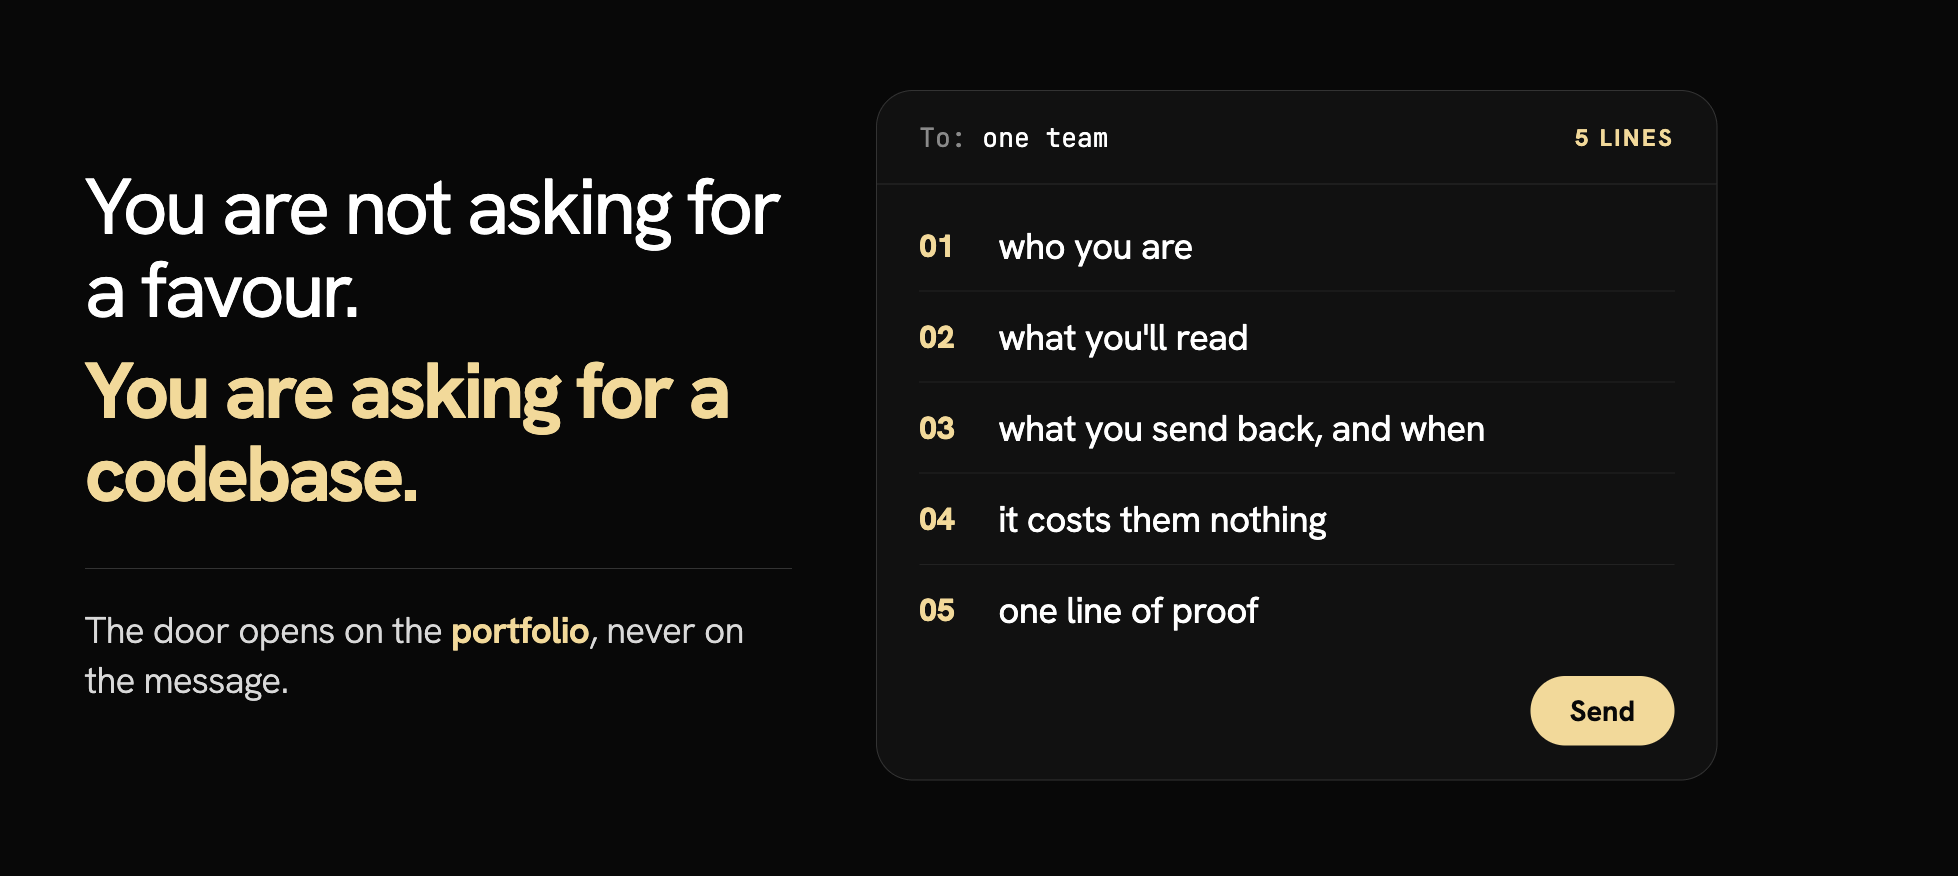
You’re not asking for a favor. You’re asking for a codebase.
It’s still what I tell people who DM me. Build a portfolio with solid bugs in it first:
free audits
unpaid bounty reports
a CTF writeup
Then message the firms.
The door opens on the portfolio, never on the message.
Your move today: write a five-line message, not a pitch deck.
Who you are
What you’ll read
What you send back, and when
That it costs them nothing
One line of proof, even a public CTF writeup
Send it to one team before you close the laptop.
Pair with one auditor stronger than you
You can’t learn what you never see.
No course shows you what a strong auditor opens first.
Or what he refuses to read at all.
I DMed a guy who had won the same $10K in the same contest.
I asked him to audit the next one together. He said yes.
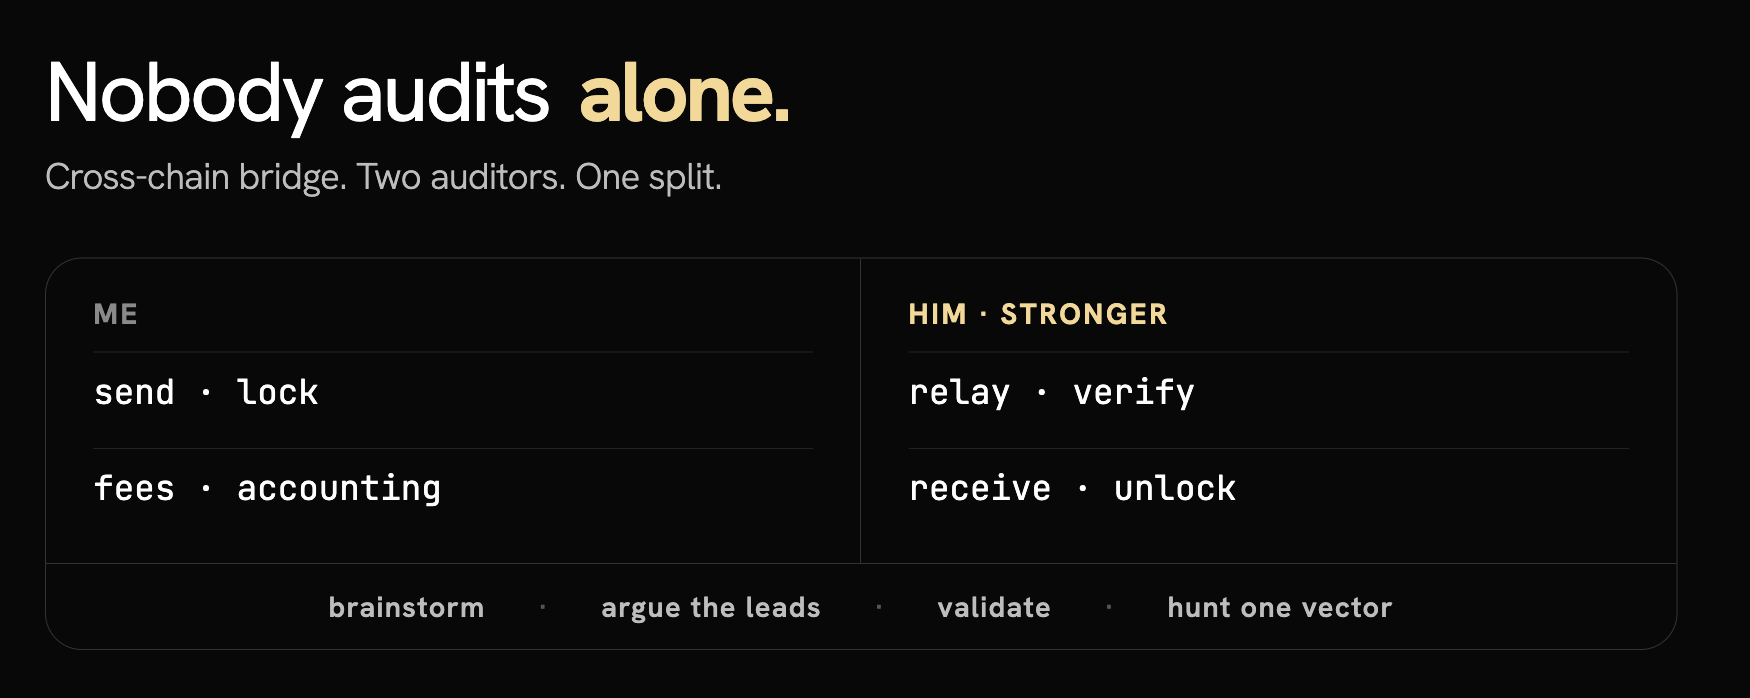
We went full time, contest after contest:
we split the flows
we argued about the leads
we ran brainstorms and validated each other’s leads
we hunted one attack vector on purpose
I watched what he opened first, and what he skipped completely.
On a cross-chain bridge we placed Top 10: one High, five Mediums, $3K.
Then we split. Both of us had taken what we needed.
The method was never the missing part.
I had the method for six months while earning nothing.
Watching someone stronger work is what moved it.
Nobody audits alone. Not the firms, not the teams, not the people making six figures a contest.
Your move today:
List three auditors ahead of you.
Message one of them about splitting the next contest.
Say which flow you’ll take. That’s the part that gets a yes.
Nobody hands you the first audit.
You take it from public code, a free offer, and one person ahead of you.
Surface to deep
I run this as a real audit, not a course:
two weeks
seven people
one live codebase with known bugs in it
Seven seats in this first run, at $299. Fewer than seven people and I refund everyone.
https://app.notion.com/p/Stop-finding-surface-bugs-3e8b025761248078af4dfbb0c5bfa7da?source=copy_link